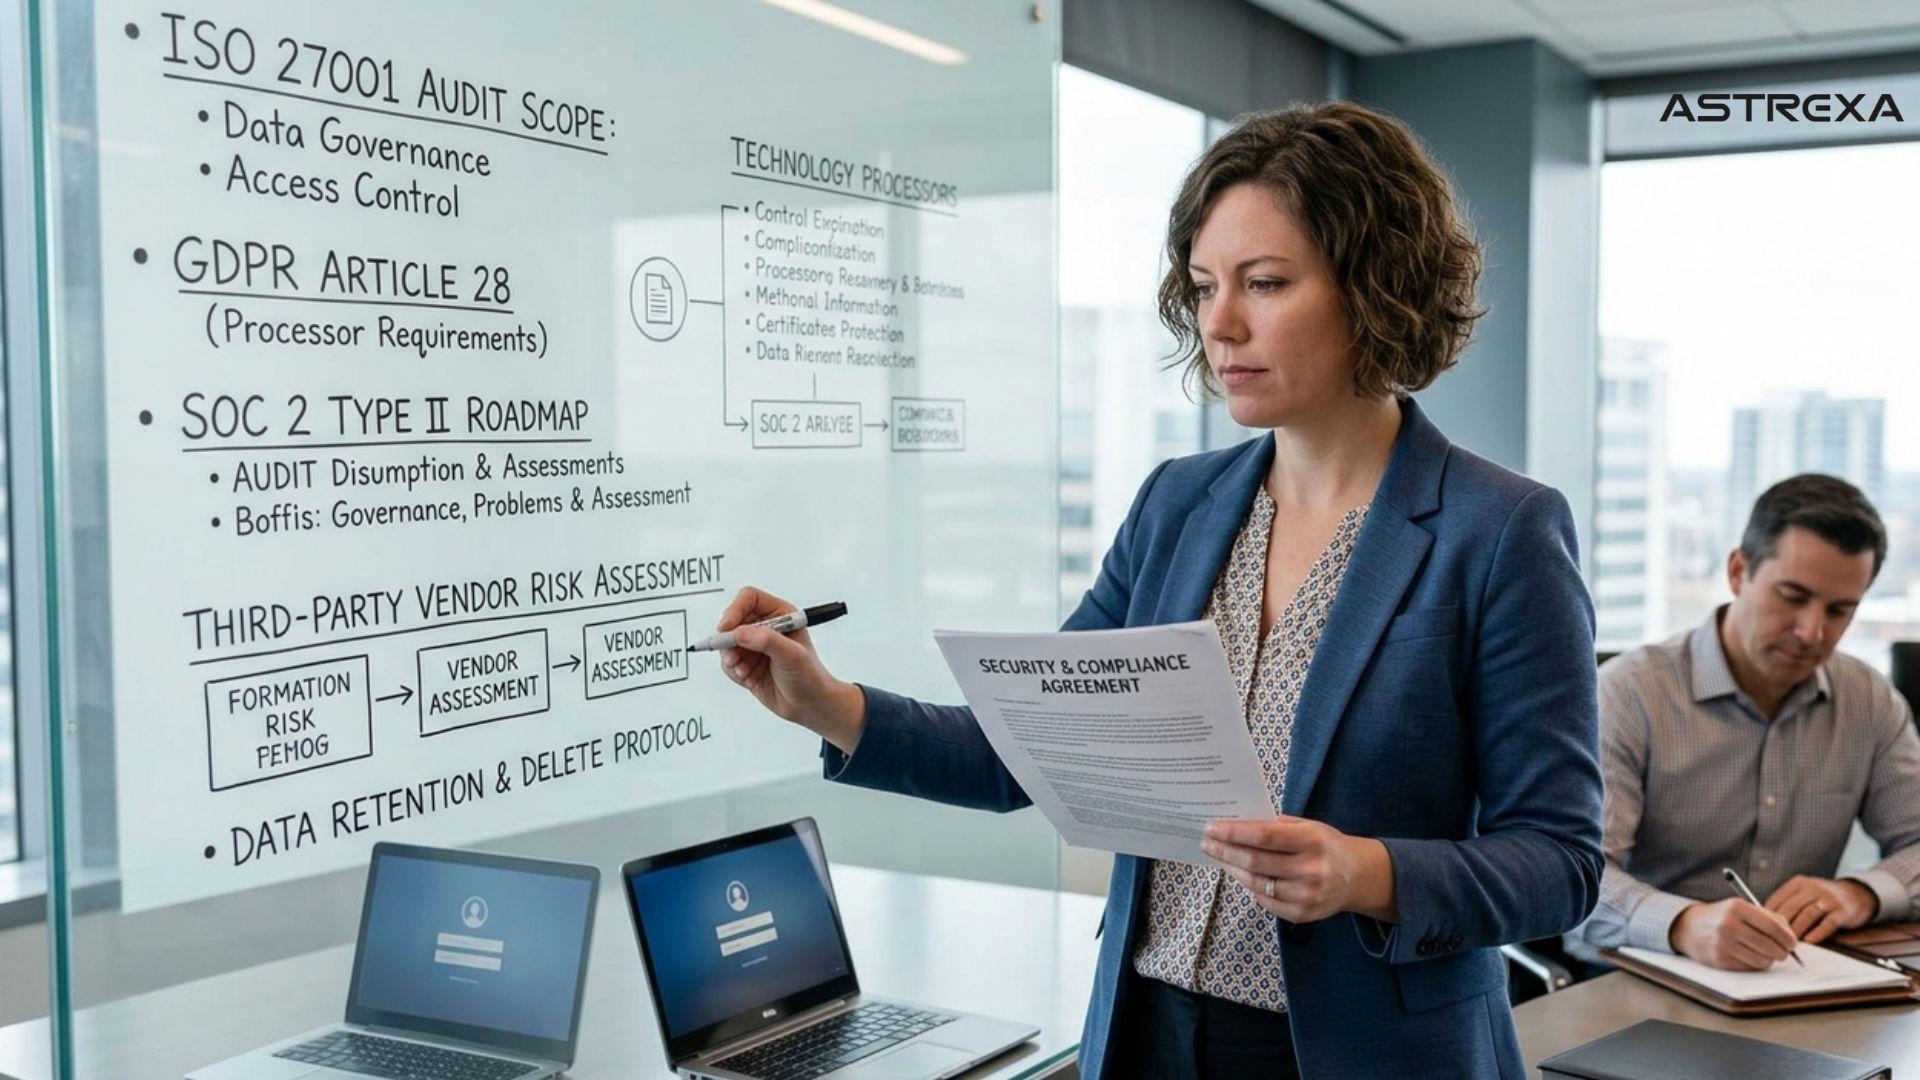
When choosing a software vendor or development partner, SMBs should ask for evidence rather than assurances: a current ISO 27001 certificate with its scope, a GDPR-compliant data processing agreement, a list of sub-processors, clarity on where data is hosted and how it moves internationally, and a clear incident notification commitment. These five items cover most of the risk for most small businesses.
Key takeaways
■ ISO 27001 certification means an independent auditor has checked a security management system — always check the certificate’s scope and validity.
■ Under GDPR, when a vendor processes personal data for you, a data processing agreement is required.
■ International transfers outside the EU and UK need an appropriate legal mechanism, such as standard contractual clauses.
■ In the UAE, federal data protection law and free-zone regimes such as those of DIFC and ADGM may also apply.
■ Ask for evidence, not adjectives.
What ISO 27001 actually tells you:
ISO/IEC 27001 is the international standard for information security management systems. Certification means an accredited auditor has assessed that the organisation has a structured approach to identifying and managing information security risks, and continues to audit it periodically.
It does not mean a vendor can never be breached. It means they have a system for managing risk that has been independently examined. Two checks matter most:
■ Scope. The certificate states which parts of the organisation are covered. Confirm that the services you are buying fall within it.
■ Validity. Certificates expire and are subject to surveillance audits. Ask for the current certificate and the certifying body.
What GDPR requires when you use a software vendor:
If a vendor processes personal data on your behalf — customer records, employee details, contact information — you are generally the controller and they are the processor. GDPR requires a written contract covering, among other things:
■ Processing only on your documented instructions.
■ Confidentiality obligations on the people handling the data.
■ Appropriate security measures.
■ Conditions for using sub-processors.
■ Assistance with data subject requests and breach notifications.
■ Deletion or return of data at the end of the contract.
This is the data processing agreement (DPA). If a vendor processing your personal data cannot provide one, that is a significant warning sign.
International data transfers:
Personal data transferred from the EU or UK to a country without an adequacy decision needs an appropriate transfer mechanism. For many vendors, this means standard contractual clauses (SCCs) incorporated into the DPA, supported by an assessment of the transfer. If your vendor or development partner is outside the EU or UK, ask how they handle this.
UAE and GCC considerations:
The UAE has a federal personal data protection law, and financial free zones such as DIFC and ADGM operate their own data protection regimes. Several GCC countries, including Saudi Arabia, have their own data protection laws. Requirements vary by jurisdiction and sector, so SMBs handling significant personal data should take local advice on which rules apply to them.
The practical checklist
Ask for | What a good answer looks like |
|---|---|
ISO 27001 certificate | Current, from an accredited body, with a scope covering the services you are buying |
Data processing agreement | Provided without delay and covering the required GDPR terms |
Sub-processor list | Named providers, their purpose and location, with notice of changes |
Data location | Clear statement of where data is hosted and whether a regional option exists |
Transfer mechanism | SCCs or another valid mechanism for data leaving the EU or UK |
Incident notification | A defined timeframe for notifying you of a breach |
Access controls | Role-based access, multi-factor authentication, access reviews |
Backups and recovery | Regular, tested backups and a stated recovery objective |
Exit terms | How your data is returned or deleted when the contract ends |
For development partners | IP assignment, confidentiality obligations and controlled access to your systems |
Proportion matters
An SMB does not need a hundred-question security questionnaire for every tool. Focus effort in proportion to the data involved: a vendor handling your customer database or production systems deserves careful scrutiny; a design tool with no personal data needs far less.
Frequently asked questions:
What does ISO 27001 certification mean?
It means an accredited auditor has assessed that an organisation operates an information security management system meeting the ISO/IEC 27001 standard, and continues to audit it. Always check the certificate’s scope and validity.
Do I need a data processing agreement with every software vendor?
Under GDPR, you need one with any vendor that processes personal data on your behalf. Vendors that handle no personal data for you do not require one.
Can a software partner outside Europe work with EU personal data?
Yes, provided an appropriate transfer mechanism is in place — commonly standard contractual clauses within the data processing agreement — and appropriate safeguards are applied.
Does GDPR apply to UAE businesses?
GDPR can apply to businesses outside the EU that offer goods or services to people in the EU or monitor their behaviour. UAE businesses are also subject to UAE federal data protection law and, where relevant, free-zone regimes.
Security you can verify
Astrexa is ISO 27001 and ISO 9001 certified and provides a data processing agreement with standard contractual clauses for European clients. Ask us for our security pack before you ask us anything else.
Written by
Nilanjan Mukherjee
Chief Executive Officer